To continuously strengthen the security of the GHOST Chain ecosystem, the core development team and ghostDAO officially invite independent security researchers, smart contract auditors, and developers to review our codebases.
While the network is currently in its testnet phase, identifying critical logic flaws, edge cases, and attack vectors early is vital to long-term stability.
Program Scope & Technical References
All repositories under the official ghostchain organization are in scope. Focus areas include:
1. Core Node & Substrate Pallets
-
Repository: ghost-node
-
Focus Areas:
-
pallets/exodus: Distributed Key Generation (DKG) / FROST threshold signature edge cases, signature rotation by previous authority sets, soft-fork safety, and unsafe HKDF usage in DKG Round 2.
-
pallets/weaver: Merkle root forging, state validation bypasses, and claim function abuse.
-
pallets/helpers: Vulnerabilities in BoundedBitmap, Merkle Tree / Hash Chain implementations, and experimental UTXO parsing logic.
-
Node Engine & Scripts: Third-party dependency flaws, RPC node configurations, bootnode setup, and automation scripts.
-
2. Smart Contracts & Bridge Logic
-
Repositories: ghost-dao-contracts, uniswap-v2-contracts, ghost-preclaims
-
Focus Areas:
-
ghost-dao-contracts: Forked/tweaked Olympus DAO logic (e.g., BondingCalculator collateral accounting risks), unfinalized authority-guarded functions leading to call-chaining exploits, legacy code execution, and Gatekeeper abstract extensions (Weaver, Historical, Verifier).
-
uniswap-v2-contracts: Compilation issues or behavior drift introduced by upgrading ported contracts to Solidity ^0.8.20.
-
ghost-preclaims: Non-deterministic execution leading to divergent state outcomes.
-
3. Frontend, Wallet & Monitoring Infrastructure
-
Repositories: ghost-eye, ghost-dao-interface, ghost-extension-wallet, ghost-lite
-
Focus Areas:
-
ghost-eye: Key management risks, server-side flaws, or data exposure.
-
Web Interfaces & Extensions: Unsafe key storage, state manipulation, calculation errors in interfaces, dependency risks, and spoofing vectors.
-
Program Rules & Guidelines
-
Public Testnet Exploitation Allowed: Security researchers are actively encouraged to execute proof-of-concept exploits on public testnet instances to prove real-world impact and feasibility.
-
Primary Reporter Priority: If duplicate issues are submitted, priority and reward rights belong exclusively to the first reporter to provide a reproducible proof-of-concept (PoC).
-
Privacy & On-Chain Payouts: ghostDAO operates under non-KYC principles. Approved bounties are transferred directly on-chain in $GMV to the wallet address supplied during triage.
Severity & Rewards
Rewards are determined based on technical impact, potential severity, and report clarity:
| Severity Level | Report Status | Reward Range ($GMV) |
|---|---|---|
| Valid Bug Report | Passed Triage | 10 – 100 $GMV |
| Invalid / Out of Scope | Failed Triage | 0 $GMV |
How to Submit a Bug Report
-
Go to GHOST Forum and navigate to the Bug Bounty category.
-
Open a new topic describing the vulnerability.
-
Do not upload file attachments. Paste relevant code snippets, execution logs, and detailed step-by-step reproduction instructions directly in standard Markdown code blocks within your post.
Triage & Governance Evaluation Process
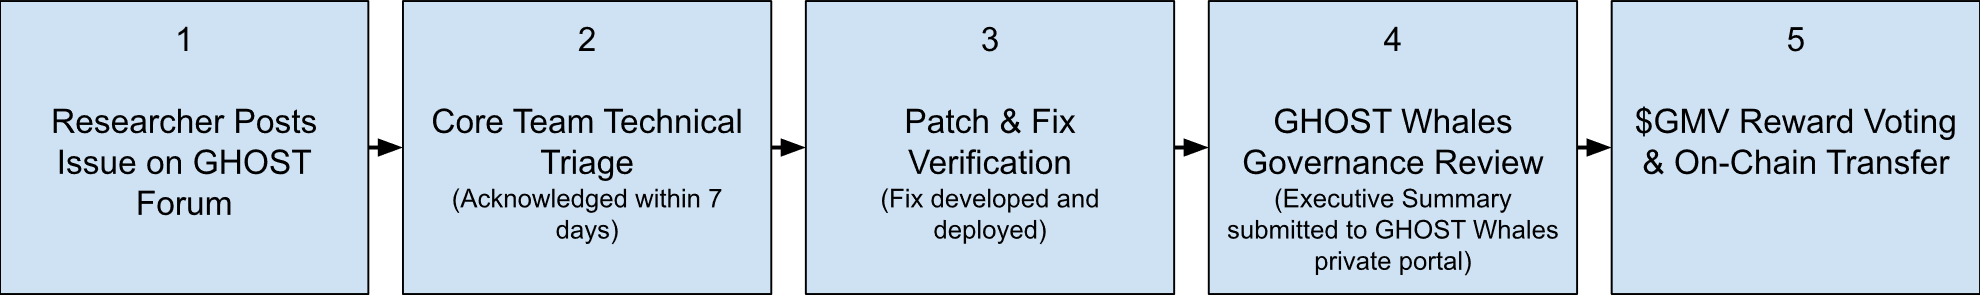
-
Acknowledgement: The core team will review and acknowledge submitted forum topics within 7 business days.
-
Remediation: Once a bug is validated, the dev team develops and applies the fix on live testnets.
-
Governance Assessment: A sanitized summary (detailing the scope and severity without revealing active exploit steps) is submitted to the GHOST Whales private governance group.
-
Payout Execution: GHOST Whales vote on the final $GMV allocation (up to 100 $GMV). Upon approval, GMV points will be awarded via ghostAidrop bot (with further swap to GMV token collateral).
Known Attack Vectors & Focus Areas
-
pallets/exodus (Repository Link)
-
Flaws in Distributed Key Generation (DKG) or FROST threshold signature scheme implementations.
-
Logic errors in validator interactions with the pallet runtime.
-
-
pallets/weaver (Repository Link)
-
Vulnerabilities allowing Merkle Root forgery or state proof manipulation.
-
Architectural defects or edge-case bugs in core Weaver logic.
-
Exploits targeting the claim function or unauthorized reward/token minting.
-
-
pallets/helpers (Repository Link)
-
Implementation bugs in BoundedBitmap boundaries and index management.
-
Structural flaws in Merkle Tree and Hash Chain verification routines.
-
State desynchronization or parsing errors in experimental UTXO logic.
-
-
ghost-node (Repository Link)
-
Vulnerabilities within underlying third-party crates or node dependencies.
-
Bugs or unsafe operations in automated deployment and node management scripts.
-
-
ghost-dao-contracts (Repository Link)
-
Logic flaws or accounting mismatches in modified Olympus DAO mechanics.
-
Access control bypasses or state flaws in Gatekeeper and its abstract extensions (Weaver, Historical, Verifier).
-
-
ghost-eye (Repository Link)
- Security flaws leading to key/credential exposure, unauthorized data access, or unexpected system behavior.
-
ghost-dao-interface (Repository Link)
-
Frontend logic flaws allowing user action spoofing or protocol abuse.
-
Mathematical/calculation errors and supply chain vulnerabilities in frontend dependencies.
-
-
ghost-extension-wallet (Repository Link)
-
Insecure key storage, memory exposure, or weak seed phrase derivation logic.
-
Transaction signing spoofing or unauthorized payload modification.
-
-
ghost-lite (Repository Link)
- Storage and cryptographic security flaws parallel to wallet extension vectors (key handling, spoofing, session hijacking).
-
uniswap-v2-contracts (Repository Link)
- Unexpected behavioral changes, overflow checks, or syntax edge cases introduced by porting legacy Uniswap V2 code to Solidity ^0.8.20.
-
ghost-preclaims (Repository Link)
- Non-deterministic execution paths leading to inconsistent state outcomes under valid input conditions.
Known Protocol Vectors & Technical Edge Cases
-
Native Coin Collateral Accounting: Potential valuation or precision errors in BondingCalculator caused by handling native blockchain currency directly as bonding collateral.
-
Authority-Guarded Call Chaining: Incomplete access controls on restricted functions, exposing vectors where unauthorized users can chain privileged function calls together.
-
Legacy Contract Exposure: Unused or deprecated smart contracts remaining in active deployment trees that could be abused as unintended entry points.
-
Experimental Gatekeeper State: Bleeding-edge logic in the latest Gatekeeper implementation that lacks full test coverage and formal verification.
-
Experimental UTXO Bridge Logic: Highly experimental inbound UTXO verification mechanics that require rigorous auditing for edge-case state desynchronization.
-
Exodus Request Pool Manipulation: Sub-optimal queue selection mechanics in the request pool that may allow malicious ordering or front-running (intended to be mitigated by GJKR and FROST/ROAST).
-
Non-Standard FROST Variant Usage: Custom adaptation of frost-core, specifically around the x-only public key variant over the secp256k1 curve.
-
EXODUS Soft-Fork Transition Risks: State inconsistencies or verification failures occurring during runtime soft-fork executions in pallets/exodus.
-
Aggressive DKG Authority Rotations: Signing authority handoffs in the final Distributed Key Generation (DKG) rounds performed by outgoing validator sets.
-
Insecure HKDF Derivation in DKG: Flaws or incorrect parameter usage in Key Derivation Function (HKDF) calls during Round 2 of the DKG protocol.
-
Randomness Seed Manipulation: Predictable or exploitable randomness generation allowing attackers to compromise ChaCha20-Poly1305 authenticated encryption states.